Express + TypeScript
Minimal Express + TypeScript integration with ServerDevTools.
See everything that happened during a backend request. Inspect request/response data, execution flow, outgoing HTTP calls, database operations, errors, and timings from one local dashboard.
npm install server-devtools
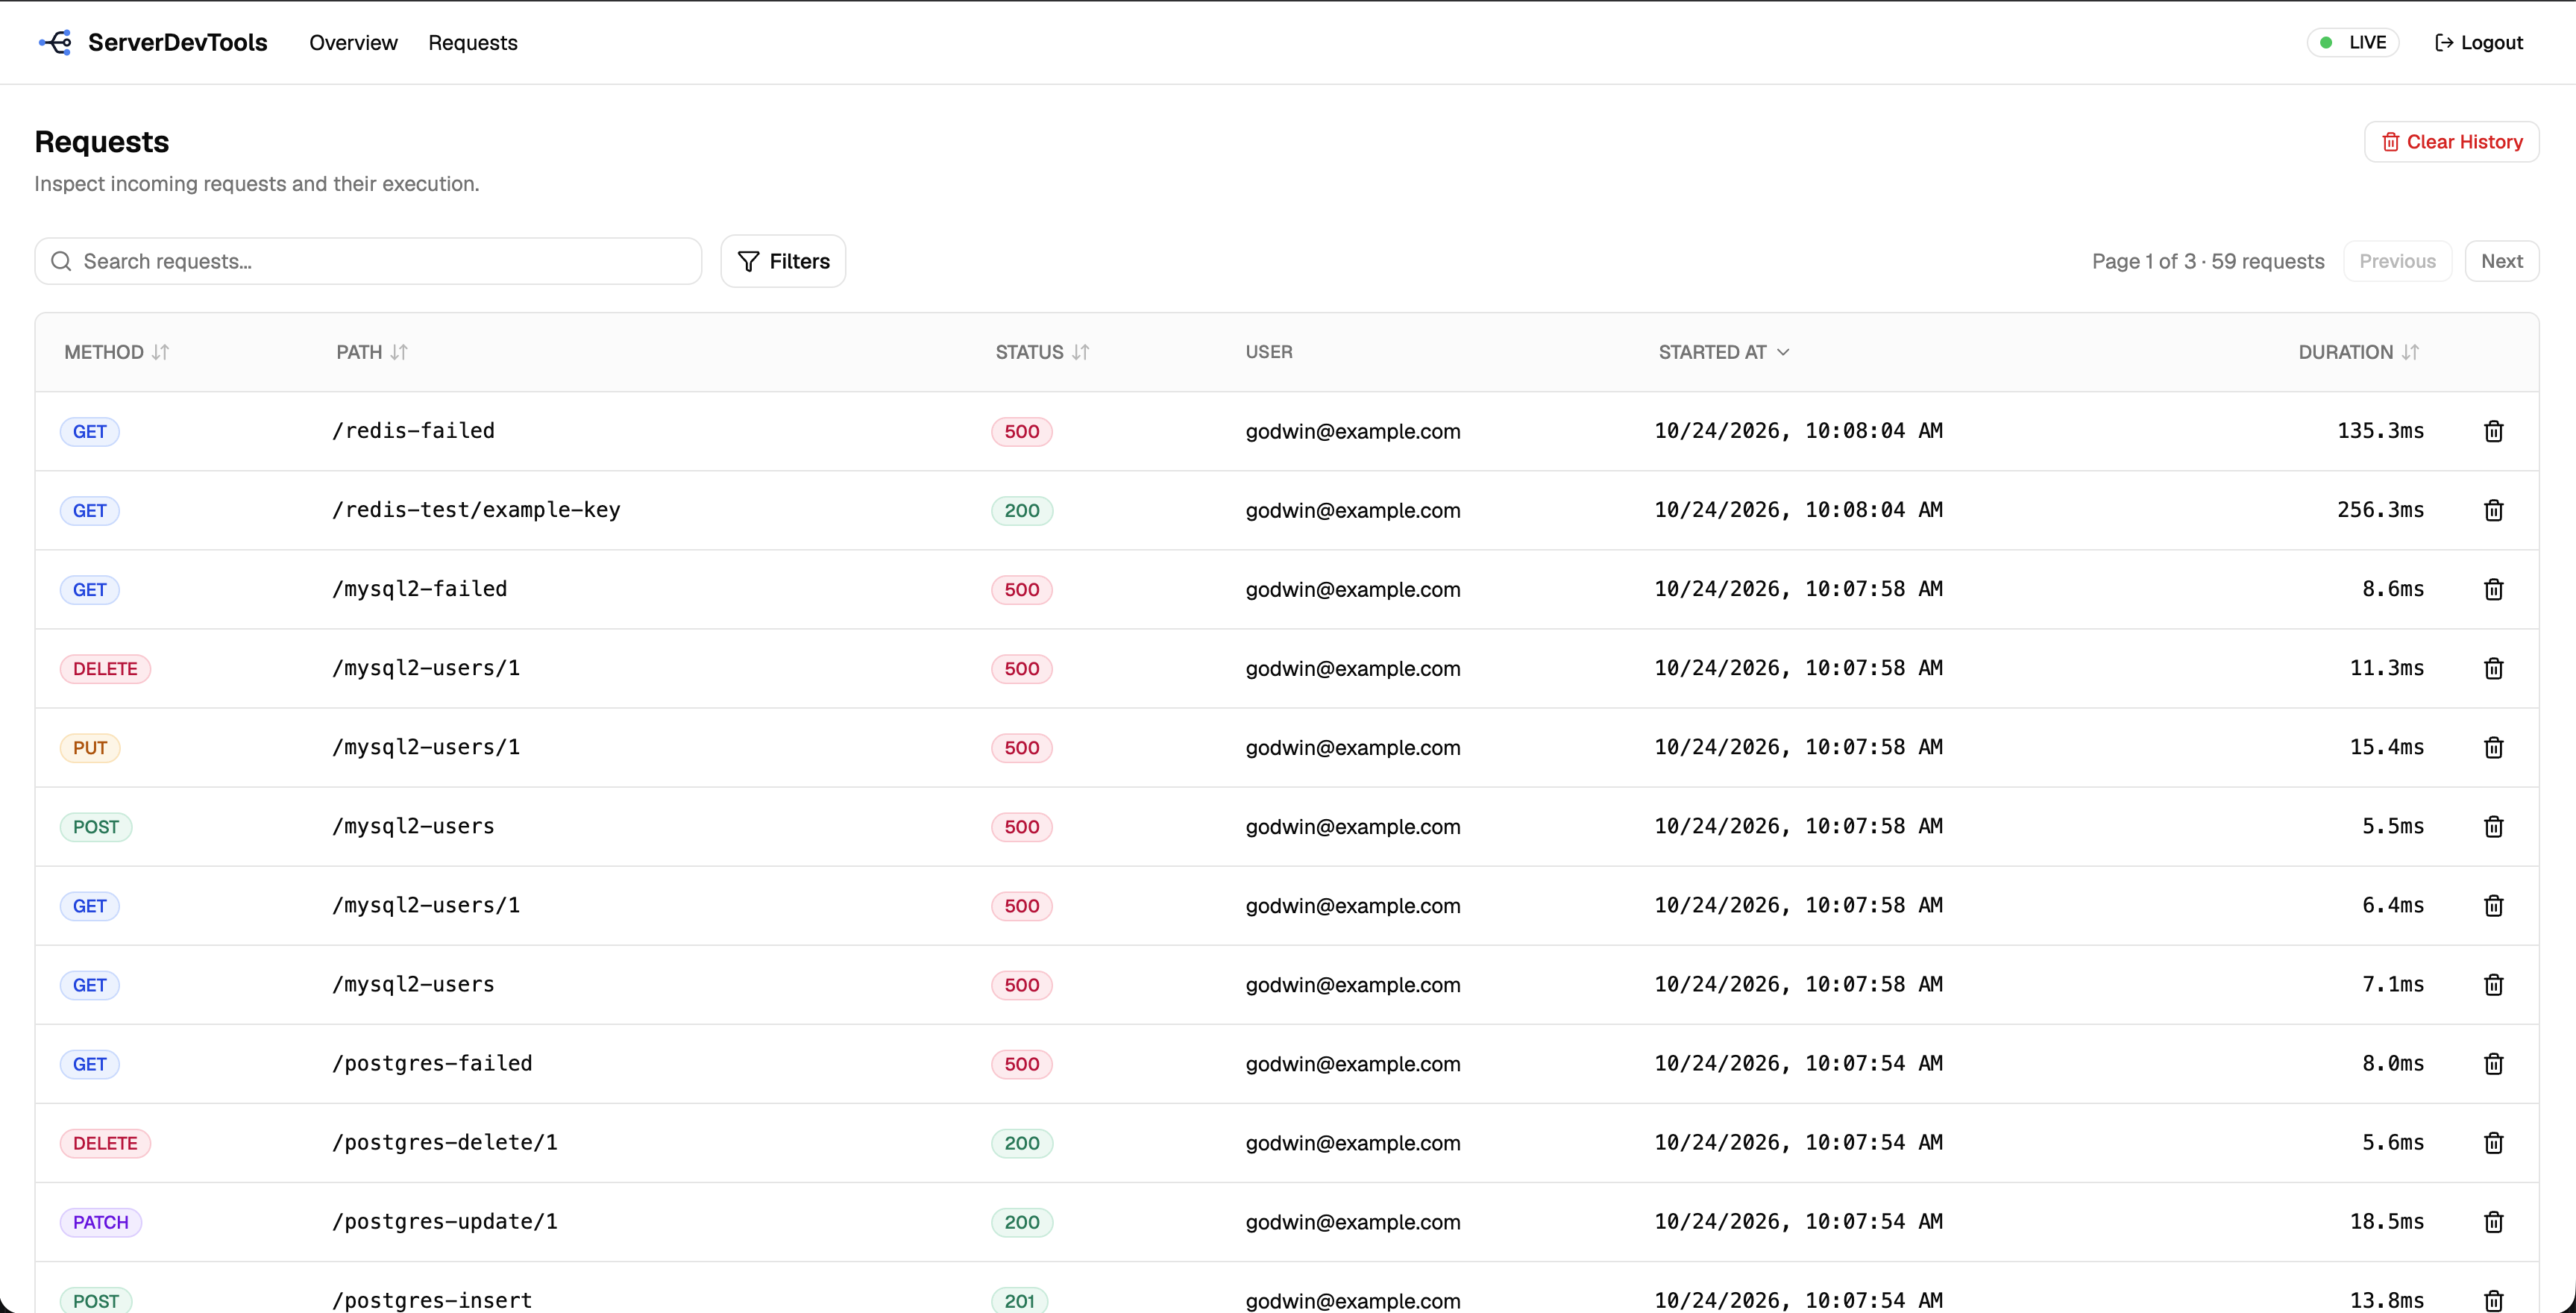
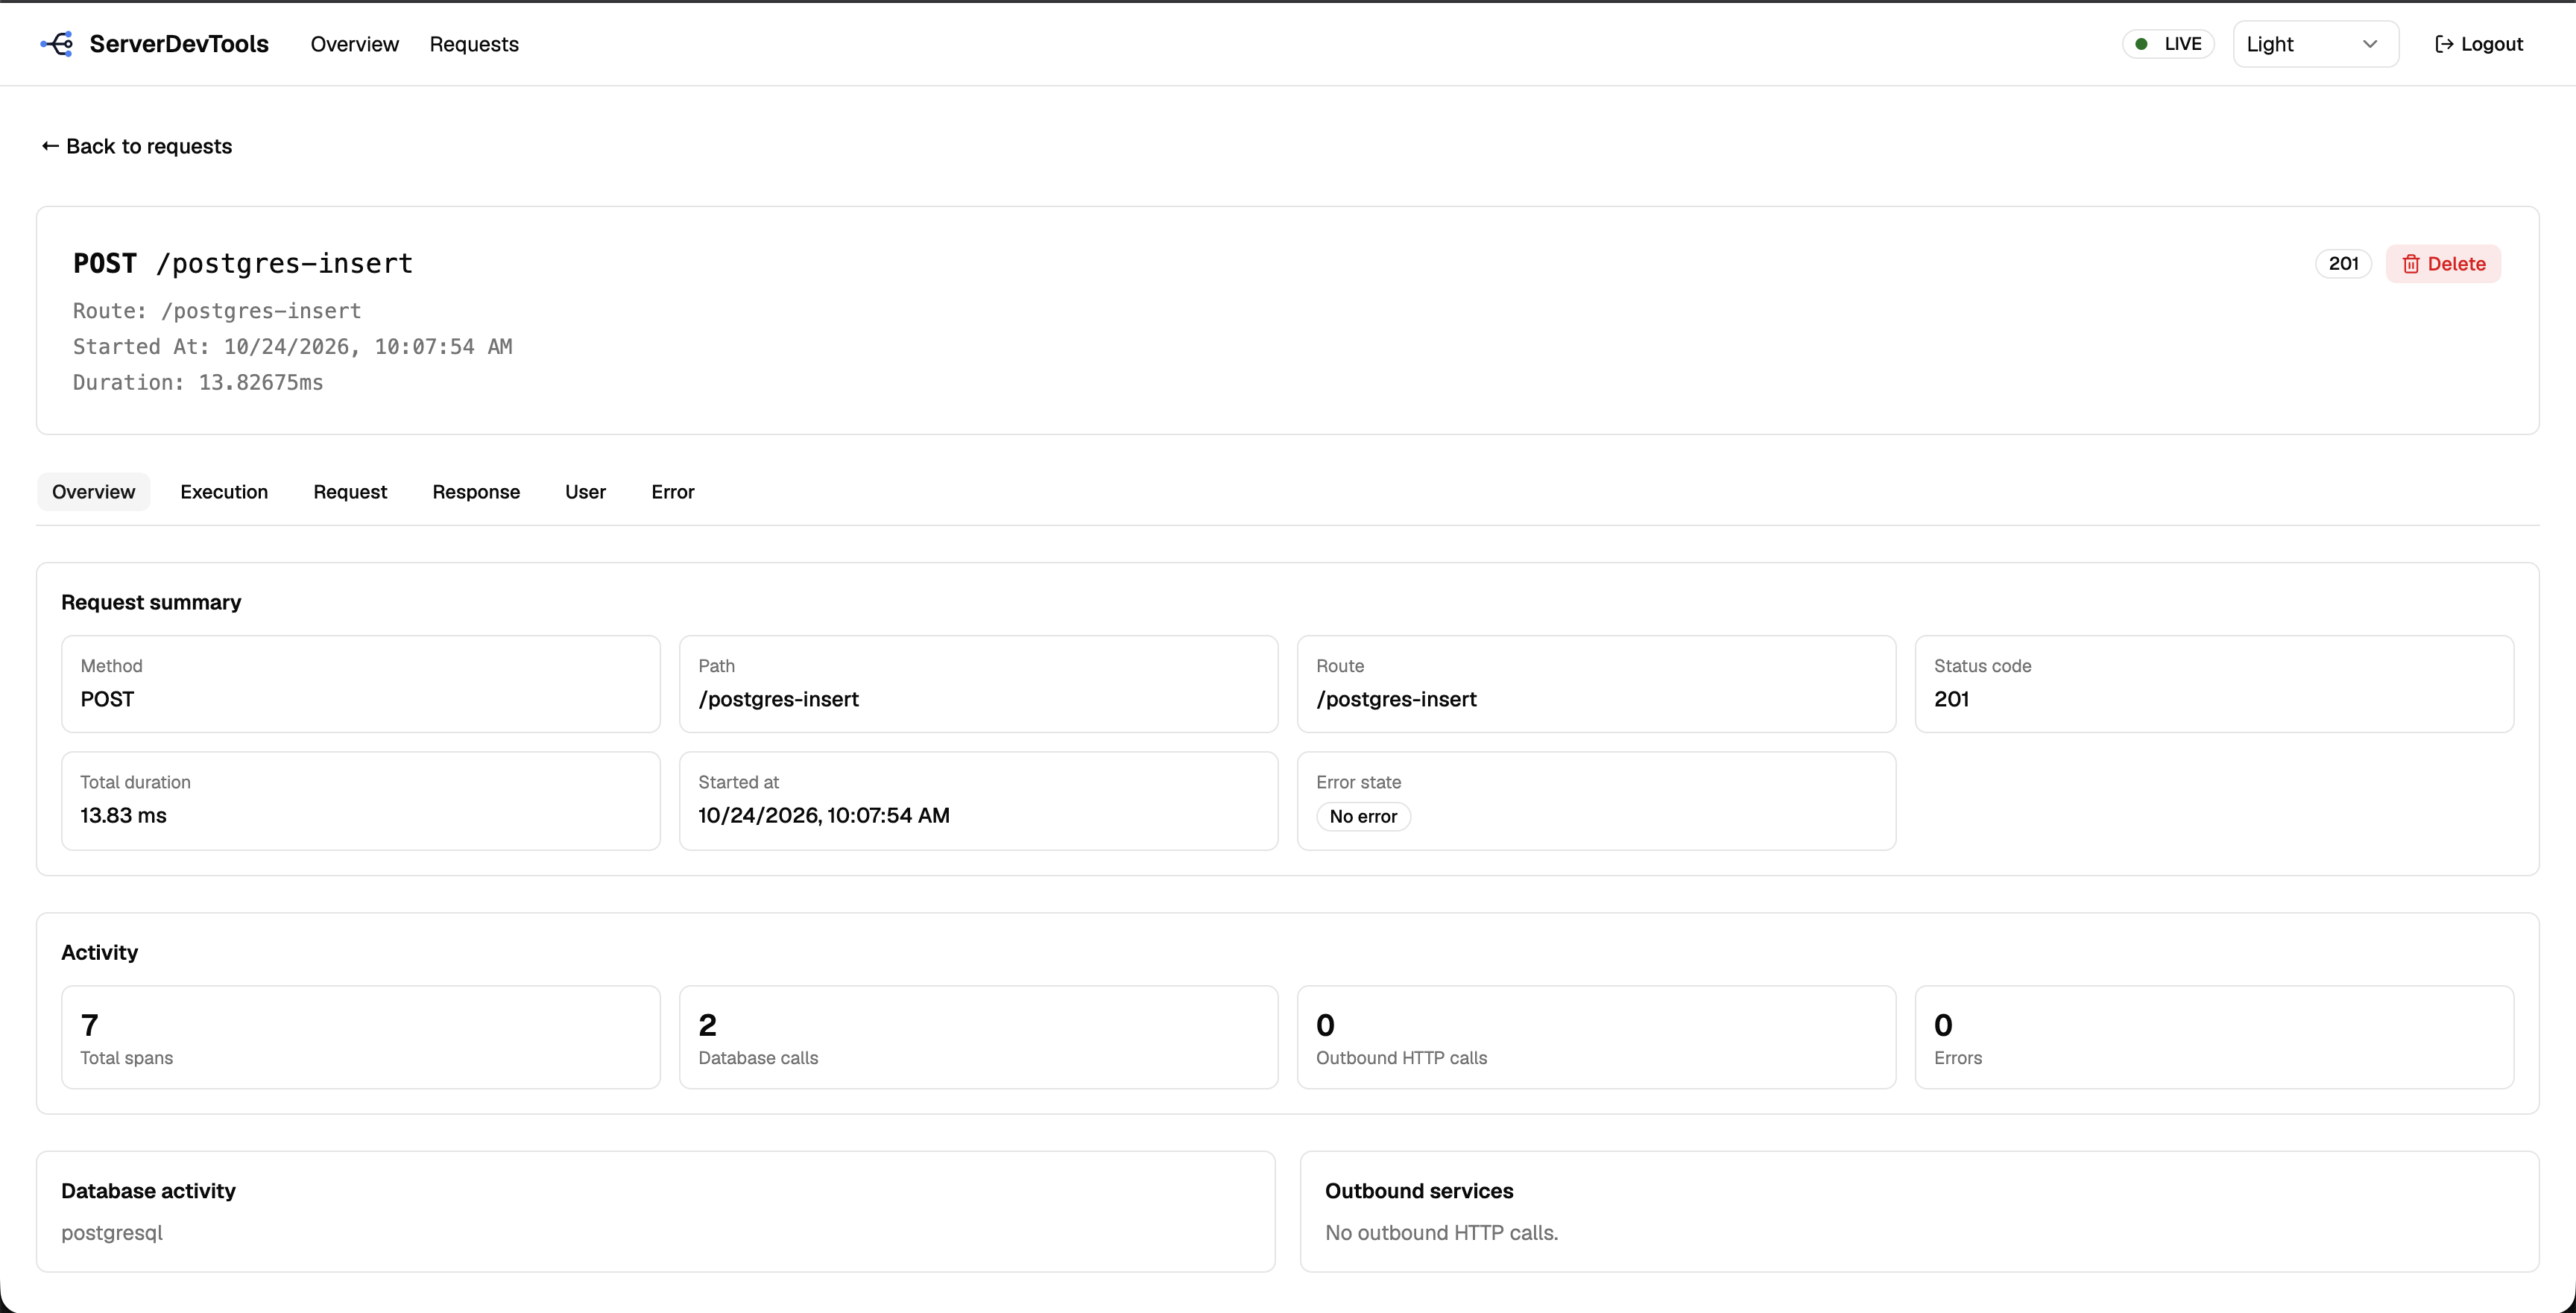
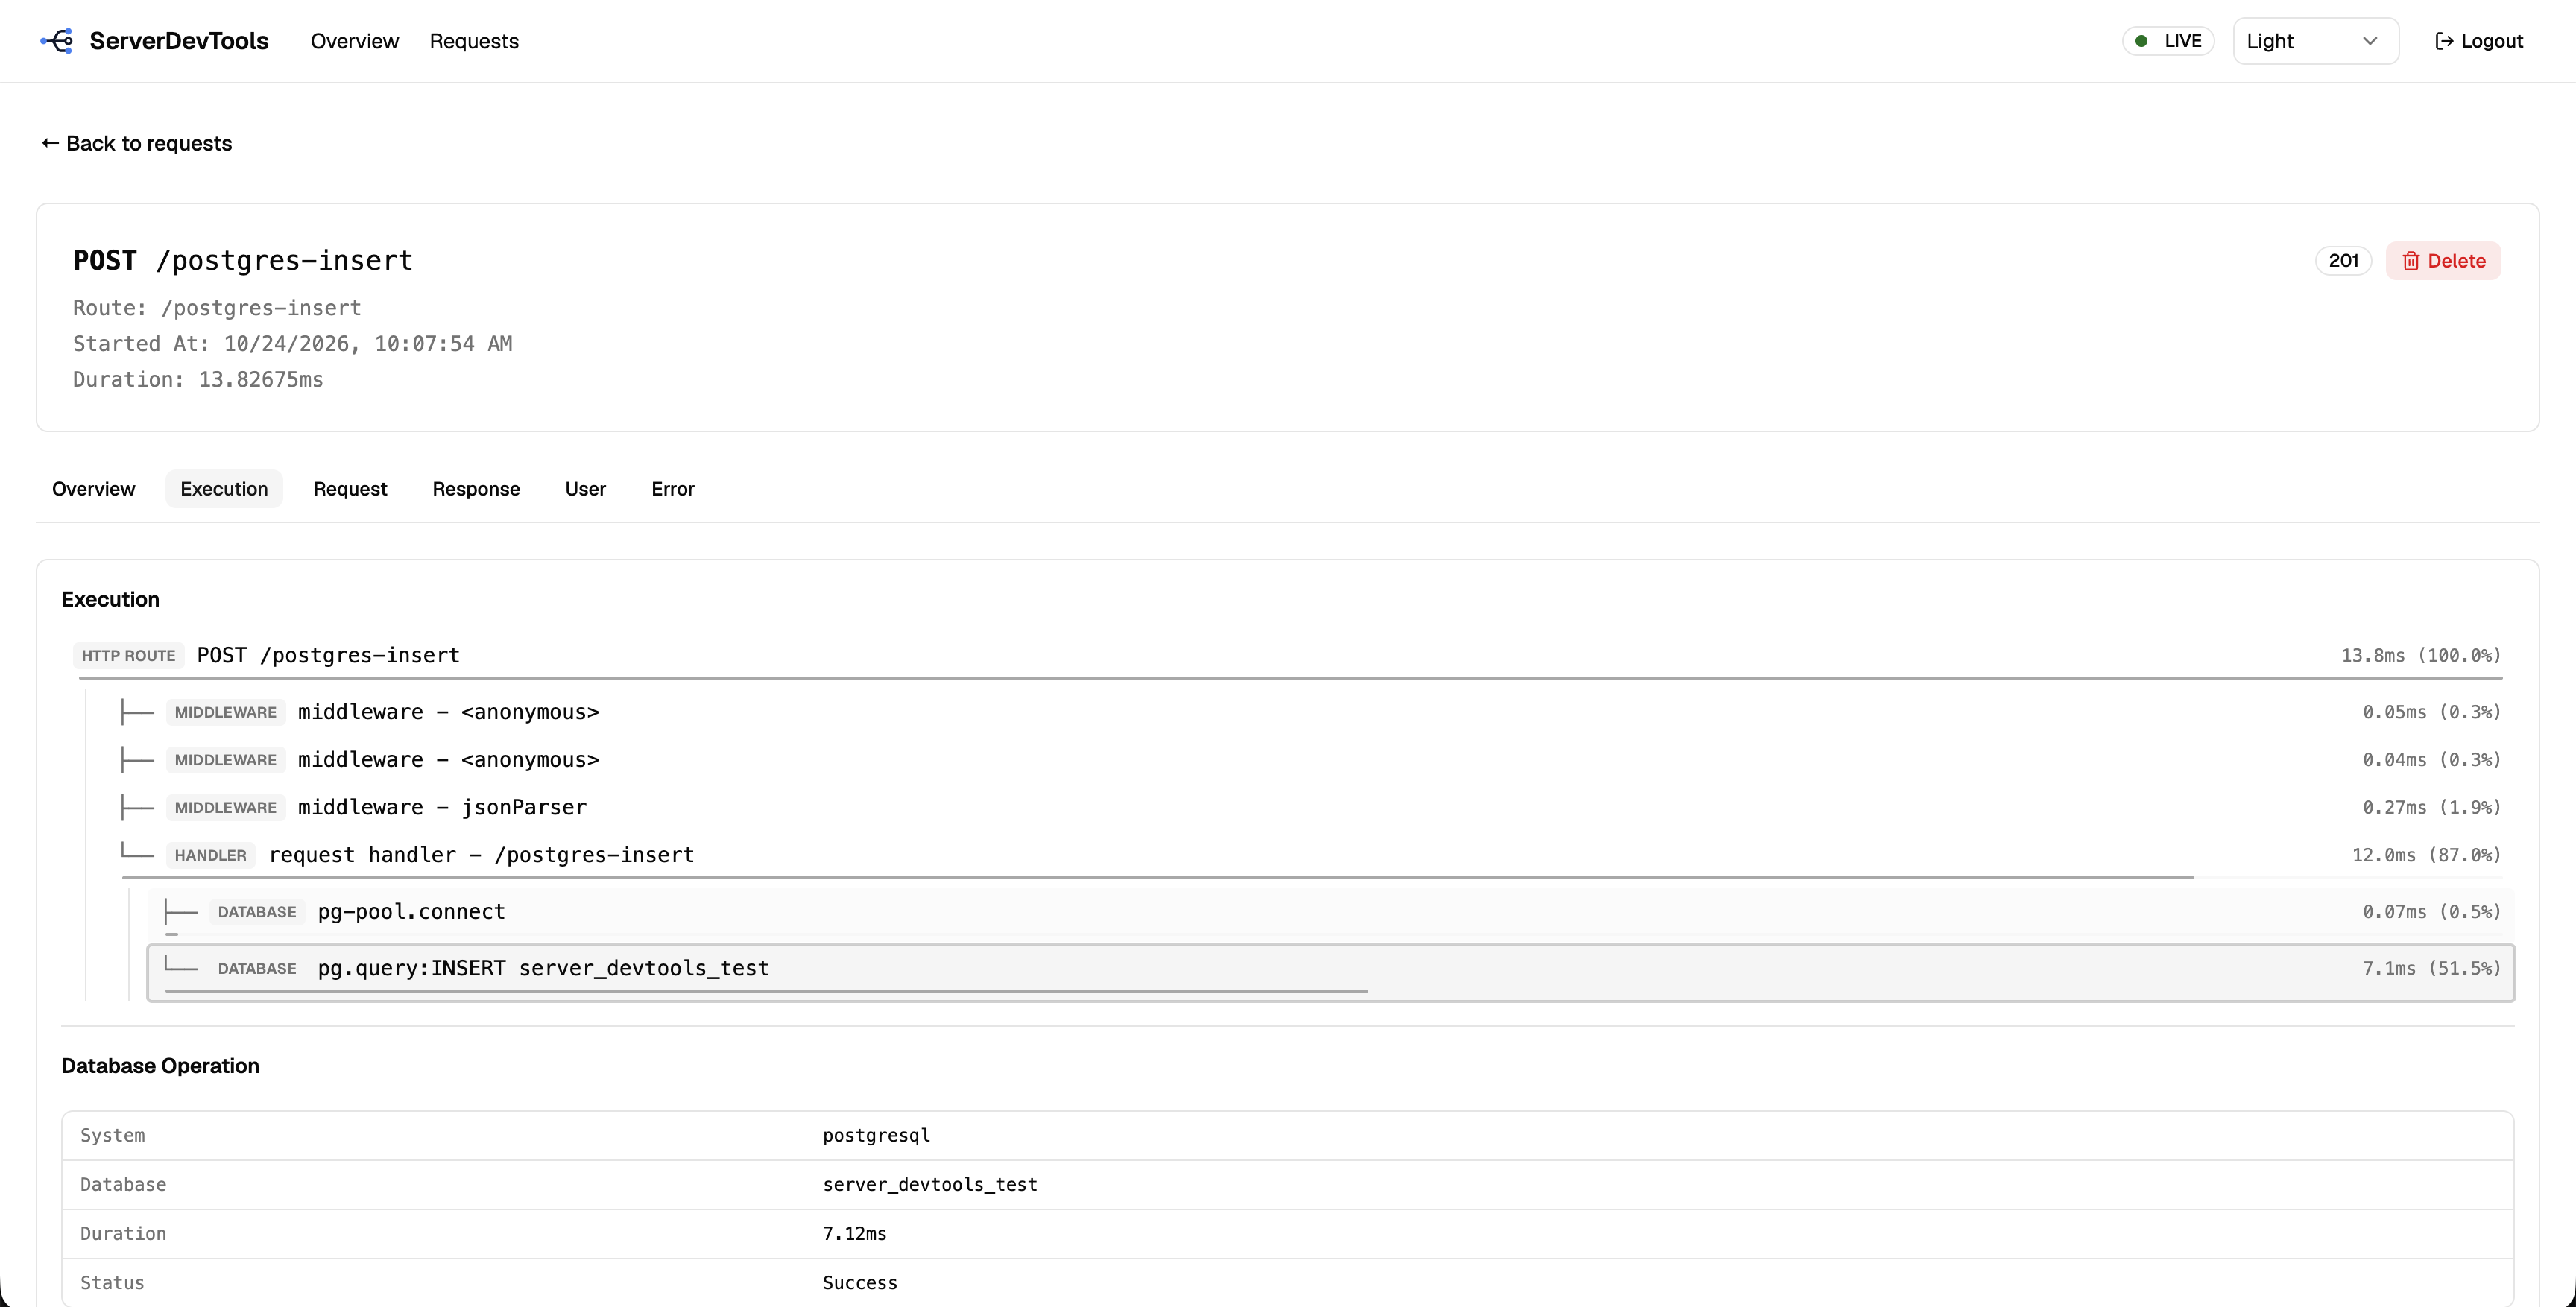
Explore the current ServerDevTools dashboard with sanitized demo data. Every slide is a static screenshot from the running dashboard—there are no simulated rows, tabs, or controls.
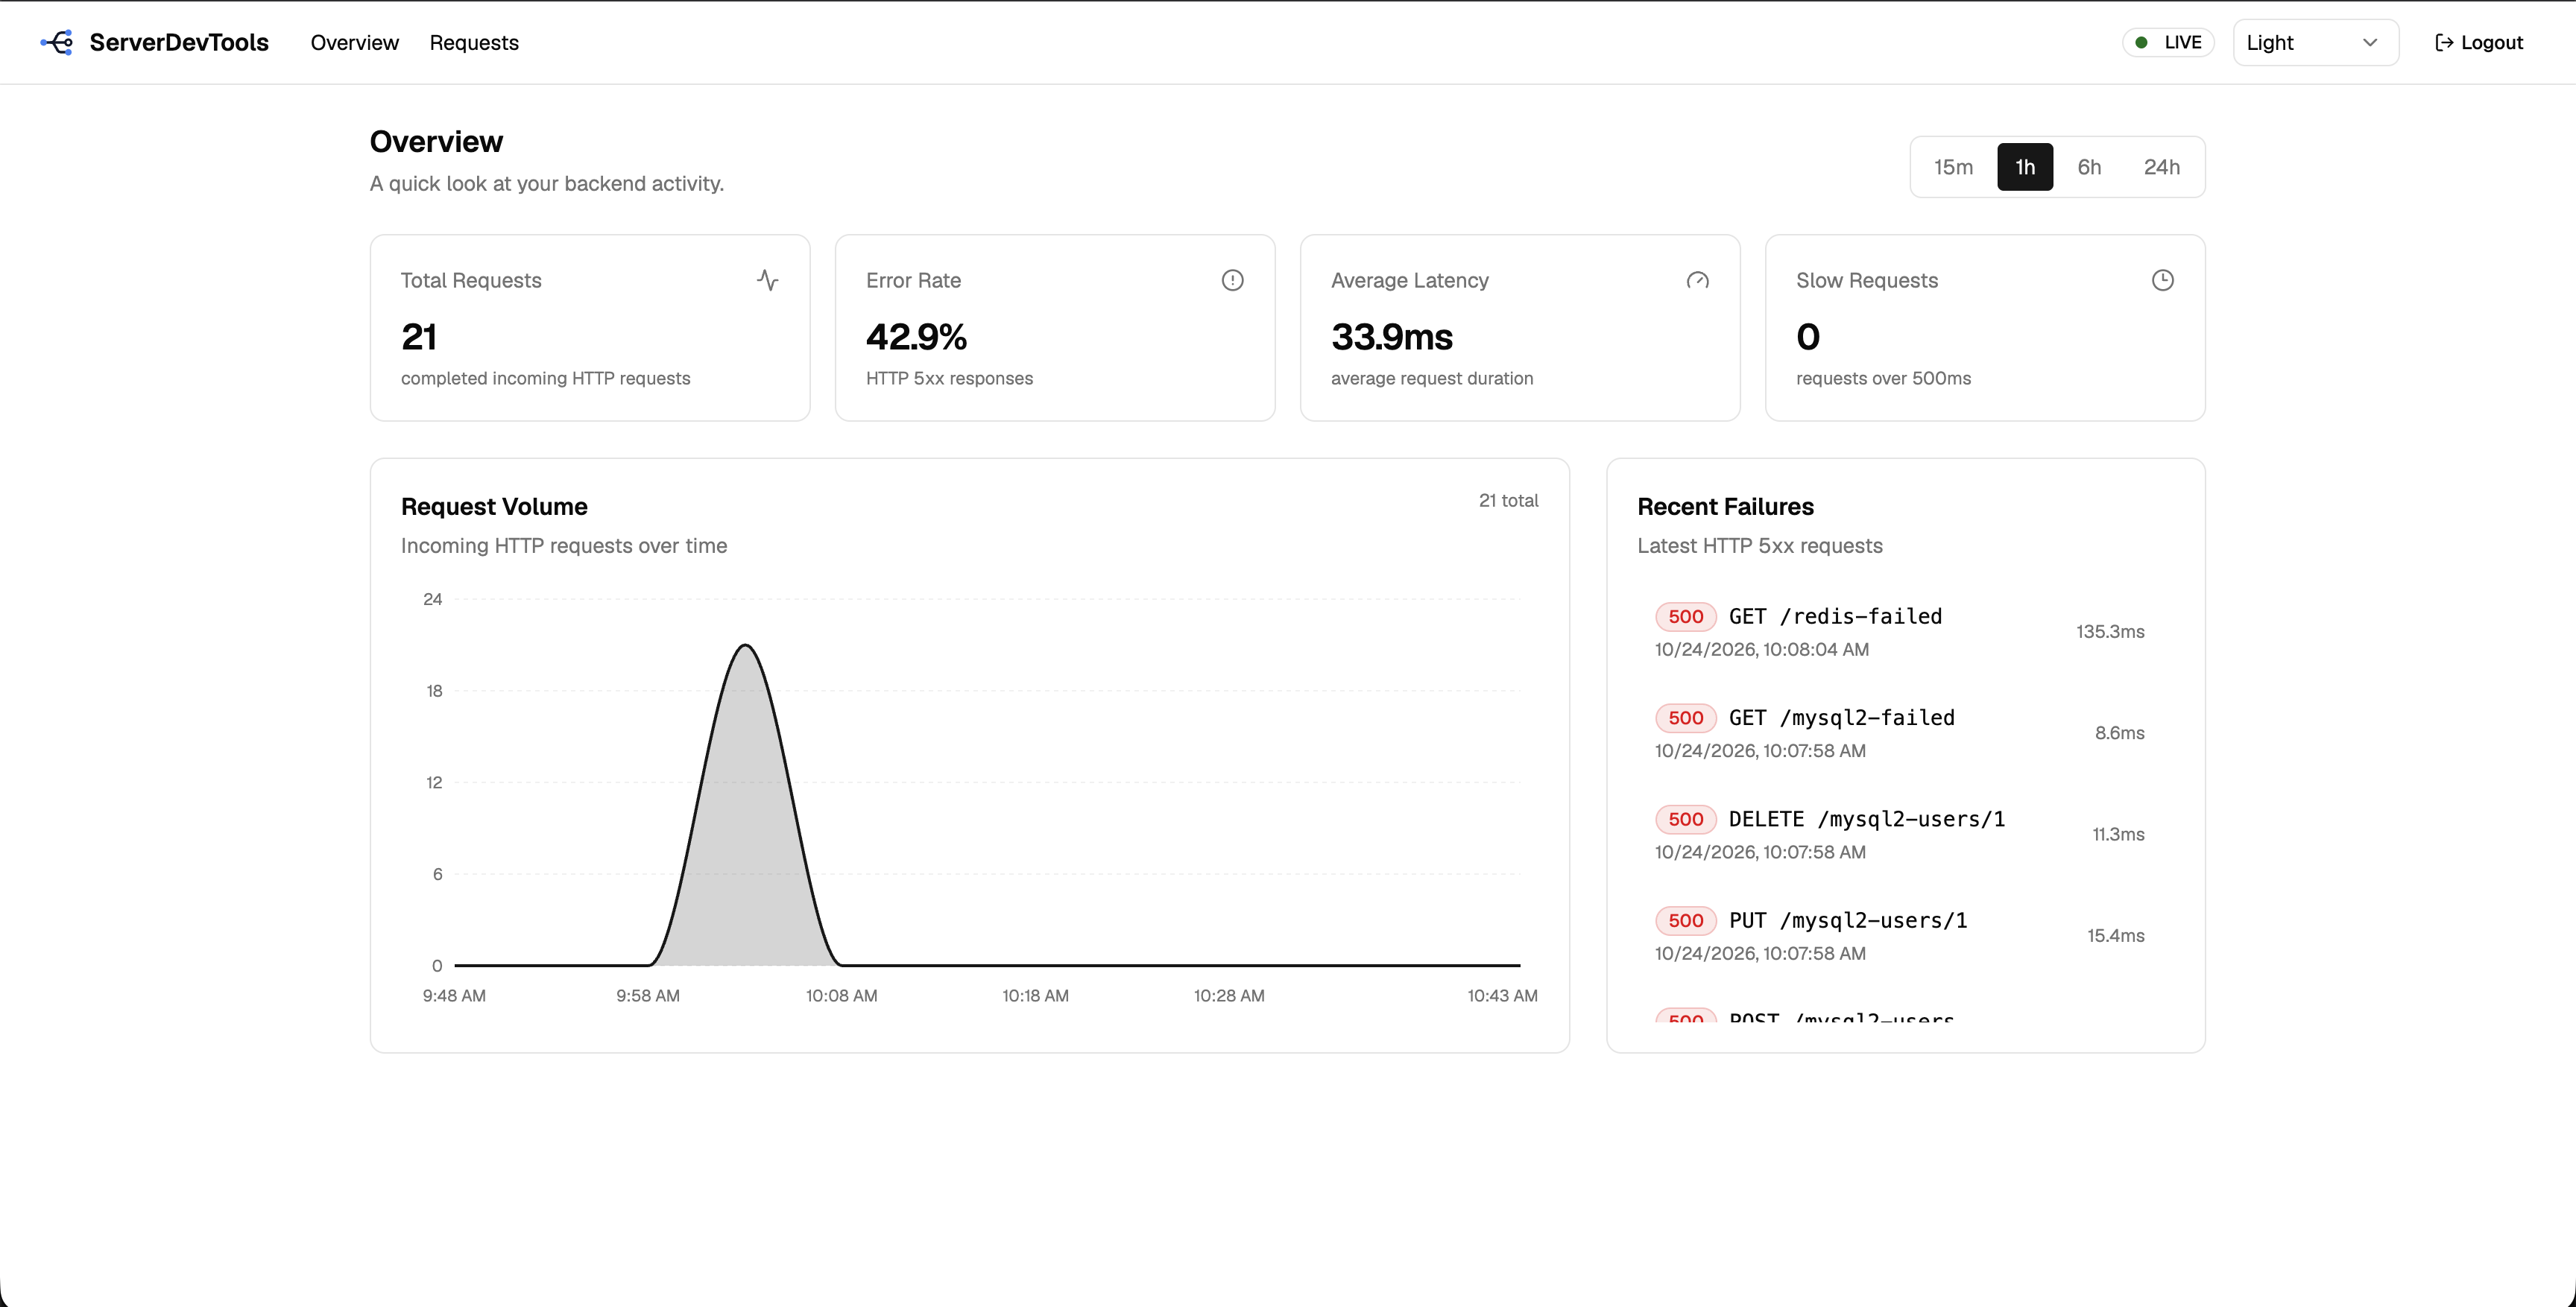
Overview — request volume, error rate, latency, and recent failures.
Captured from the current local dashboard with sanitized demo data. The Requests view has no matching dark asset, so it remains unchanged in Dark mode while its surrounding frame follows the selected theme.
Mount the middleware in your existing Node.js application and open its dashboard at /_devtools.
Add the developer instrumentation package to your project. Supported OpenTelemetry database instrumentation is included.
Create and start your own initialization file, then preload it before your application starts. Choose any filename and location.
Import that same instance in your application, mount its middleware, and open /_devtools to inspect requests.
Inspect method, route and path parameters, query parameters, request headers and body, and response headers, body, and status.
Follow middleware, handlers, database operations, and outbound calls within a request.
Inspect MongoDB, PostgreSQL, MySQL (`mysql2`), and Redis (ioredis) operations and their timing inside the request trace. Redis (ioredis) spans include command inspection, request-linked spans and timings, and command errors, with support verified in Express and NestJS, including pipelines and transactions.
Inspect outbound native Node.js HTTP/HTTPS and fetch/Undici calls, including request and response headers and bodies.
Inspect request-associated errors with available message, type, and stack information.
See duration across the request execution tree and compare operation timings.
ServerDevTools runs inside your Node.js application, instruments backend activity, persists inspection history to SQLite, and serves its dashboard from your existing HTTP server without requiring a separate ServerDevTools web server.
/_devtools
// server-devtools.ts
import ServerDevTools from "server-devtools";

export const devtools = new ServerDevTools({
  auth: {
    username: process.env.SERVER_DEVTOOLS_USERNAME!,
    password: process.env.SERVER_DEVTOOLS_PASSWORD!,
  },
});

await devtools.start();

// src/main.ts
import { createServer } from "node:http";
import { devtools } from "../server-devtools";

const server = createServer((req, res) => {
  devtools.middleware(req, res, () => {
    res.end("ok");
  });
});

server.listen(3000);

// npx tsx watch --import ./server-devtools.ts src/main.ts
// server-devtools.ts
import ServerDevTools from "server-devtools";
export const devtools = new ServerDevTools({
auth: {
username: process.env.SERVER_DEVTOOLS_USERNAME!,
password: process.env.SERVER_DEVTOOLS_PASSWORD!,
},
});
await devtools.start();
// src/main.ts
import express from "express";
import { devtools } from "../server-devtools";
const app = express();
app.use((req, res, next) => devtools.middleware(req, res, next));
app.get("/health", (_req, res) => res.json({ ok: true }));
app.listen(3000);
// npx tsx watch --import ./server-devtools.ts src/main.ts// server-devtools.js
const ServerDevTools = require("server-devtools");
const devtools = new ServerDevTools({
auth: {
username: process.env.SERVER_DEVTOOLS_USERNAME,
password: process.env.SERVER_DEVTOOLS_PASSWORD,
},
});
globalThis.__serverDevtools = devtools;
void (async () => {
await devtools.start();
})();
// tsconfig.json
{
"compilerOptions": {
"allowJs": true
}
}
NODE_OPTIONS='--import ./server-devtools.js' nest start --watch
// src/main.ts
import { NestFactory } from "@nestjs/core";
import { AppModule } from "./app.module";
import { ServerDevToolsNestInterceptor } from "server-devtools/nestjs";
import ServerDevTools from "server-devtools";
declare global {
var __serverDevtools: ServerDevTools | undefined;
}
async function bootstrap() {
const devtools = globalThis.__serverDevtools;
if (!devtools) {
throw new Error(
"ServerDevTools was not preloaded. Start Nest with NODE_OPTIONS='--import ./server-devtools.js'.",
);
}
const app = await NestFactory.create(AppModule);
app.use((req, res, next) => devtools.middleware(req, res, next));
app.useGlobalInterceptors(
new ServerDevToolsNestInterceptor(),
);
await app.listen(3000);
}
bootstrap();Start from a working integration or use it as a reference for your own application.
Minimal Express + TypeScript integration with ServerDevTools.
Minimal NestJS integration with the recommended ServerDevTools preload setup.
When an endpoint fails or slows down, see the HTTP request, full execution path, database queries, Redis (ioredis) commands, external network calls, and errors correlated together.
console.log("here 1")
http://localhost:3000/_devtools
ServerDevTools can capture request and response metadata, selected headers and bodies, user context when configured, database operations, and outbound HTTP activity when the relevant instrumentation and request context are present. It stores traces in ./server-devtools.db by default and does not send telemetry to a ServerDevTools service.
Default header redaction covers authorization, proxy-authorization, cookie, set-cookie, and x-api-key; additionalHeaders extends that list. Optional AES-256-GCM encryption protects configured fields at rest; it is not whole-database encryption. Read the data-handling guidance →
Instrumentation adds span creation and persistence work. Native outbound request and response body capture skips bodies above 256 KiB without changing the network payload; inbound response and fetch capture have no SDK byte limit today. No reproducible benchmark is published, so measure in your own environment.
An in-process Node.js request inspection dashboard for seeing request lifecycles, timings, database operations, outbound calls, and errors during development.
Postman sends and tests API requests, while Swagger documents an API contract. ServerDevTools observes what your running backend actually did during a request.
It is a local, in-process inspection tool rather than a hosted monitoring platform. It focuses on request detail and a local SQLite history instead of fleet-wide monitoring.
The SDK requires Node.js 20 or newer and documents native Node HTTP, Express, and NestJS integrations, plus MongoDB, PostgreSQL, MySQL, Redis, and outbound HTTP instrumentation.
The SDK has no ServerDevTools telemetry service or collector; it writes to local SQLite. Outbound instrumentation observes your application’s own calls and does not export them to ServerDevTools.
Yes. Bodies, URLs, query parameters, headers, database attributes, errors, and user data can contain sensitive values. Header-name redaction is enabled for the documented defaults and can be extended with redaction.additionalHeaders; it does not cover bodies, URLs, queries, or arbitrary span attributes. Optional encryption protects configured fields at rest. See the security guide.
By default, traces are stored in ./server-devtools.db. Use Clear History in the dashboard or delete individual traces; there is no automatic trace retention policy.
Native outbound request and response body capture has a fixed 256 KiB limit. Oversized bodies are skipped rather than truncated, while the complete application network payload continues to its destination. Other body paths do not currently have an SDK byte limit.
OpenTelemetry patches supported libraries during startup. Preloading ServerDevTools before those imports lets the instrumentations register before requests or database clients are created.
Server-Timing is a response header for exposing selected server durations to a client. ServerDevTools stores a richer server-side trace with request, database, outbound, and error details.
See how an in-process request inspector compares with an API client and a hosted observability platform.
Planned capabilities, not available yet:
Store ServerDevTools data through user-configured storage instead of only the default local SQLite file.
Free and open source. Embed the inspector in your Node.js application and inspect activity in development, staging, or deployed environments.